
Lars Seufert
Senior Advisor
Governance-focused security leader with 15+ years of experience across organizations of all sizes, elevating risk management, resilience, and business alignment in a fast-paced, rapidly evolving landscape.
LinkedIn →
Team
Dan Gorecki leads every engagement. Senior advisors with the same operator background join when the work needs more than one set of hands.
The principal
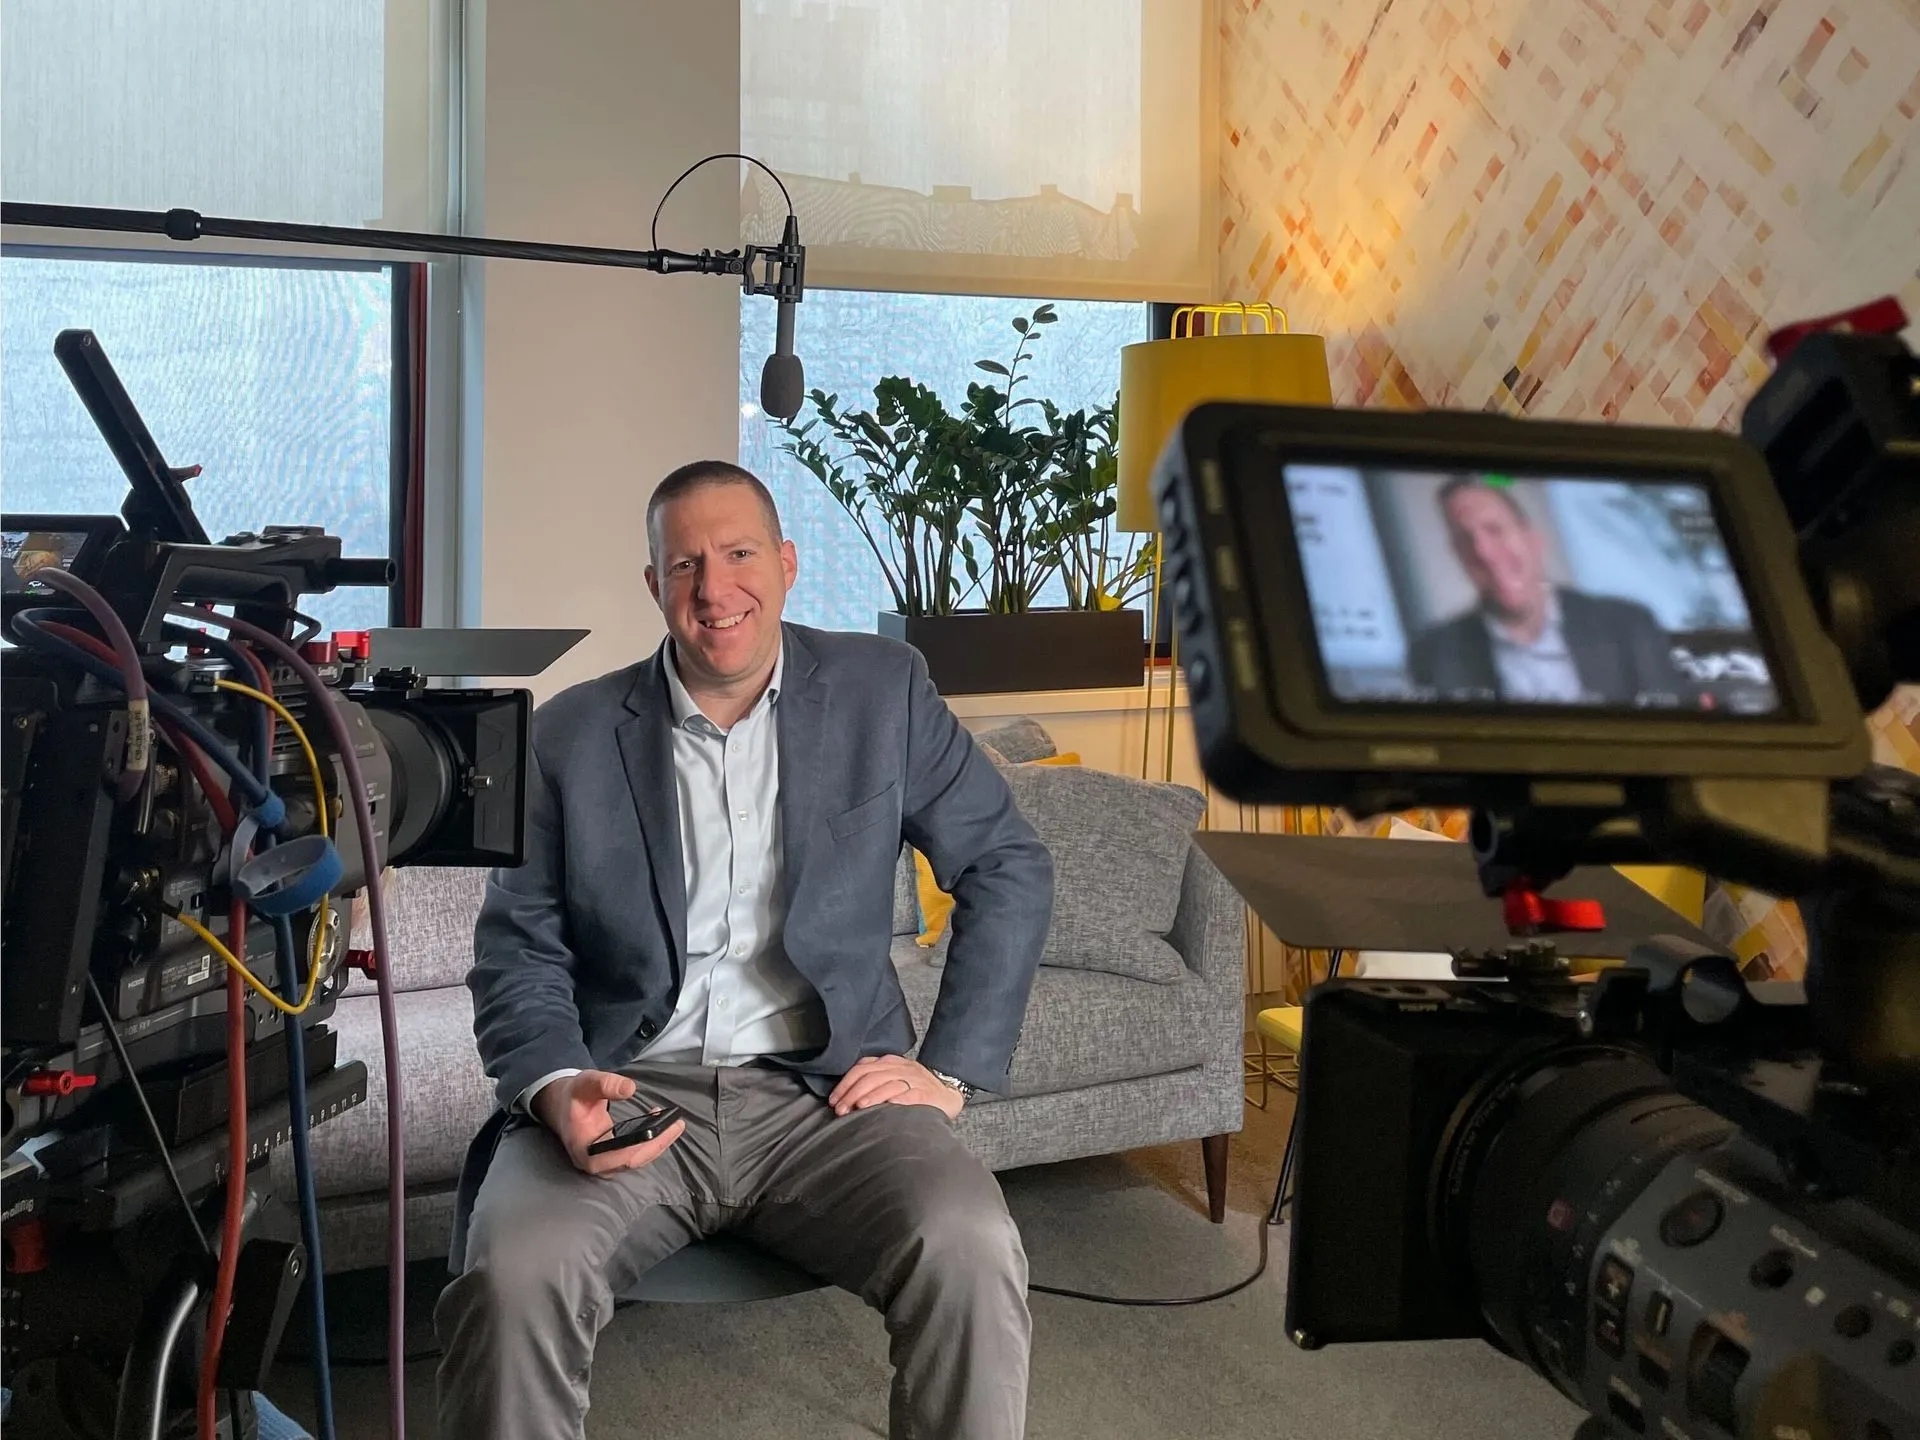
Principal, Chief Risk, Resilience & Trust Officer
Dan brings more than twenty years in technology and a decade of global cyber and risk leadership to NGC Risk. He has held CIO and CISO seats, at times both at once, at organizations from 30-person startups to a Fortune 200, building risk-based, resilient programs that earn C-suite and board support.
His career spans heavily regulated industries: hedge funds, manufacturing and biopharma, hospitality, insurance, and fintech. That’s where he learned how cyber, technology, and operational risk actually meet, and how much rigor a business can carry before it slows down.
Dan works alongside leadership. He sizes programs to the organization’s risk appetite and maturity, which means avoiding over-engineering as much as unnecessary exposure. Clients describe him as collaborative and transparent, and allergic to compliance theater.
Dan is co-chair of RSAC’s CISO Boot Camp for 2027, preparing future CISOs for the role, after co-chairing RSAC’s Cyber Leader Forum in 2025 and 2026. He also co-chairs SIM’s DigiRisk special interest group, a forum for IT leaders working through new technology risk, and is a member of the UK Cyber Security Council’s Technical Working Group, helping draft and review industry standards for cyber security careers.
The bench
Lars Seufert
Senior Advisor
Governance-focused security leader with 15+ years of experience across organizations of all sizes, elevating risk management, resilience, and business alignment in a fast-paced, rapidly evolving landscape.
LinkedIn →
Bob McSheffery
Manager of Strategic Partnerships
Bob has built his career in sales and business development, developing relationships and helping organizations work through complex business challenges. He works with clients to understand their cybersecurity and risk priorities and connects them with practical help, from Fractional CISO services to a risk register that sets priorities, assigns ownership, and drives accountability. His approach is relationship-first, built on what he calls pleasant persistence: showing up, listening carefully, and following through.
LinkedIn →Start a conversation
Tell us what’s prompting the call: a board question, an AI rollout, an audit finding, or an empty seat. We’ll take it from there.